Questions or Concerns?

If you want more detail about our services, your privacy or how we handle data, you can contact us through our website.

Data Processing Agreement

Last Updated: 1st of December, 2025

This Data Processing Agreement (“DPA”) forms part of the Terms of Service or any other written or electronic agreement between the Customer (“Controller”) and Avista (“Processor”) for the use of Avista Care and Avista Chat (the “Services”).

This DPA ensures compliance with the EU General Data Protection Regulation (GDPR) and governs how Avista processes personal data on behalf of the Customer.

1. Definitions

“Controller” means the Customer who determines the purposes and means of processing personal data.
“Processor” means Avista, which processes personal data on behalf of the Controller.
“Personal Data” means any information relating to an identified or identifiable natural person.
“Processing” means any operation performed on personal data, such as collection, storage, transmission, or deletion.
“Sub-processor” means any third-party processor engaged by Avista.
“Services” means Avista Care (website maintenance & monitoring) and Avista Chat (AI chatbot services).
2. Scope of Processing
Avista processes personal data solely for the following purposes:

Avista Care

  • Website monitoring, updates, backups, and performance services
  • Logging and diagnostics
  • Security scanning
  • Customer support

Avista Chat

  • Training and operating chatbots using customer-provided data
  • Handling prompts, messages, logs, and uploaded documents
  • Monitoring usage and performance
  • Providing support and analytics
  • Avista processes data only according to the Controller’s documented instructions.

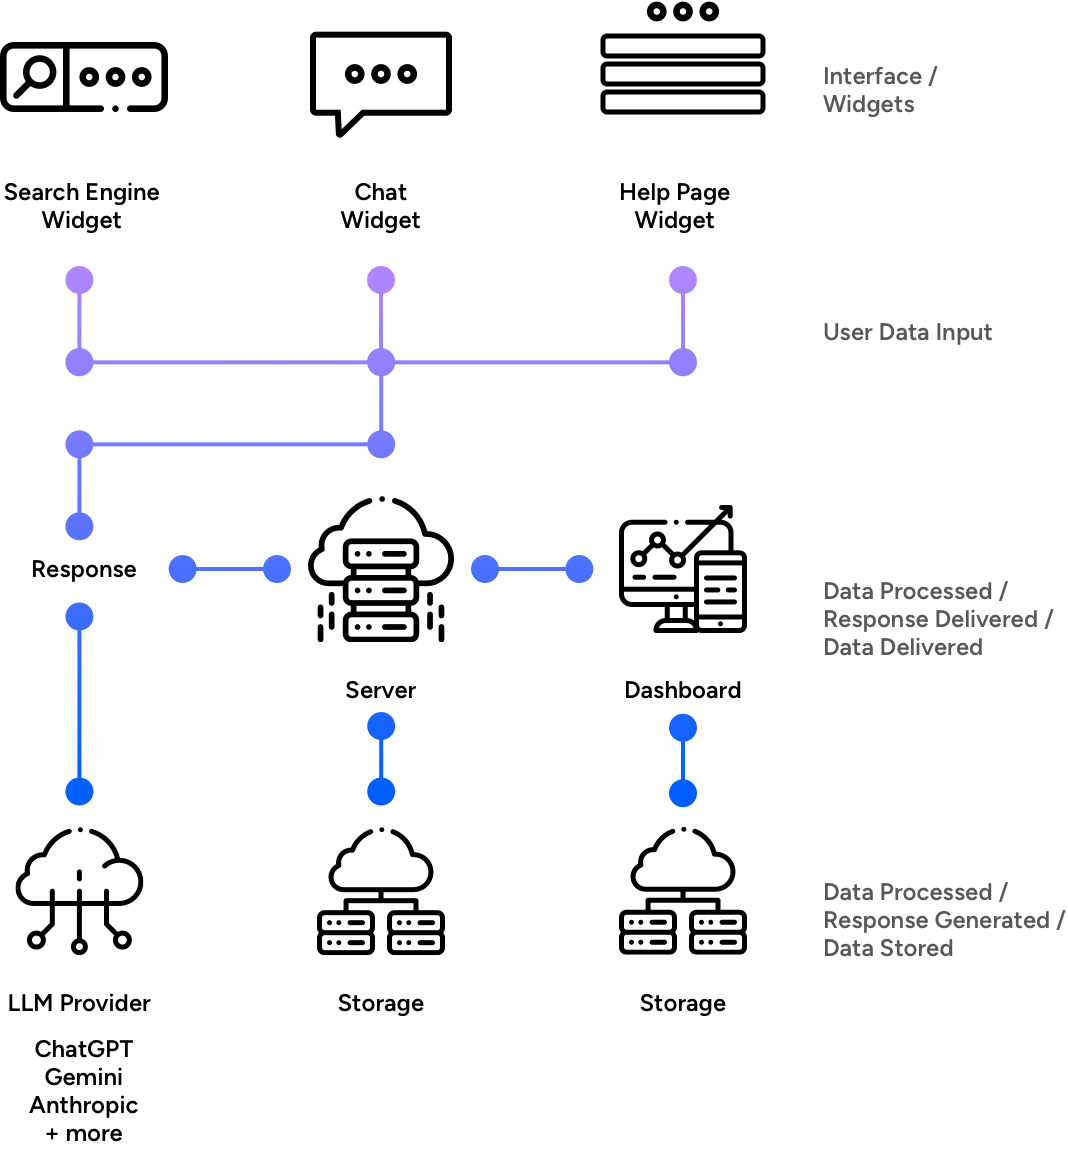
Overview of Avista Chat data flow:
3. Types of Data Processed

Depending on the Services used, Avista may process:

  • Contact details (e.g., name, email)
  • Website metadata (domains, logs, security scan results)
  • Backup data and content from Customer websites
  • Chat messages, uploaded documents, or AI training inputs (Avista Chat)
  • Technical information (IP addresses, browser data, error logs)
  • Billing information (handled by payment processors)
  • Avista does not use Customer data to train external AI models or for advertising.

4. Duration of Processing

Processing continues for the duration of the Customer’s subscription and is limited to what is needed to deliver the Services. Upon termination, Avista deletes or anonymizes data in accordance with Section 10.

5. Obligations of the Processor (Avista)

Avista agrees to:

  • Process data only on Controller’s instructions
  • Maintain confidentiality
  • Implement appropriate technical and organizational security measures
  • Assist the Controller in fulfilling GDPR obligations
  • Notify Controller of data breaches without undue delay
  • Keep updated records of processing activities
  • Ensure employees and contractors follow security and privacy policies

6. Sub-Processors

The Controller authorizes Avista to use Sub-processors for hosting, backups, monitoring, AI inference, analytics, and support tools.

Avista will:

  • Only engage GDPR-compliant Sub-processors
  • Ensure each Sub-processor is bound by equivalent data protection obligations
  • Publish or provide a list of Sub-processors upon request
  • Inform the Controller of any significant changes to Sub-processors
  • The Controller may object to a Sub-processor on reasonable grounds.

7. Obligations of the Controller (Customer)

The Controller agrees to:

  • Ensure their processing instructions comply with GDPR
  • Provide data that they have the right to process
  • Not upload unlawful or sensitive personal data unless necessary
  • Maintain accurate configuration and access controls
    Inform Avista of any inaccuracies or corrections needed

8. Data Subject Rights

Avista will assist the Controller in responding to requests such as:

  • Access
  • Rectification
  • Erasure
  • Portability
  • Restriction
  • Objection
  • Avista will not respond directly to the data subject unless instructed by the Controller.

9. Security Measures

Avista implements industry-standard measures including:

  • Encryption in transit
  • Encrypted storage for backups
  • Secure access controls and authentication
  • Regular security monitoring
  • Segmented infrastructure
  • Data minimization
  • Least-privilege access policies
  • A full description of measures can be provided upon request.

10. Return or Deletion of Data

When the Service ends:

  • Access to dashboards is removed
  • Backups are deleted after retention expires
  • Personal data is erased or anonymized within a reasonable period
  • Logs may be retained temporarily for security or compliance
  • The Controller may request accelerated deletion.

11. International Transfers

If data is transferred outside the EEA:

  • Avista uses GDPR-approved safeguards such as Standard Contractual Clauses (SCCs)
  • Only processors with adequate protection levels are engaged
  • Transfers comply with applicable laws

12. Breach Notification

If Avista becomes aware of a data breach affecting Customer data, Avista will:

  • Notify the Controller without undue delay
  • Provide available information on the nature of the breach
  • Support the Controller in fulfilling notification duties

13. Audits & Compliance

Avista will provide documentation needed to demonstrate compliance
Formal audits may be requested with reasonable notice
Audits must respect confidentiality and technical boundaries

14. Liability

Both parties’ liability follows the main Terms of Service.
Avista is only liable for processing operations under its direct control.

15. Governing Law

This DPA is governed by the laws of Iceland and applicable EU/EEA data protection regulations (including GDPR).

Privacy Policy

Last updated: 5th of January, 2026

Your privacy matters to us. This Privacy Policy explains what information Avista collects, how we use it, and the choices you have. By using Avista Care (the “Service”), you agree to the practices described here.

1. Information We Collect

We collect information to deliver and improve the Service. This includes:

1.1 Information you provide

  • Account details (name, email, billing information)
  • Website information (domain, configuration settings, installed plugins/themes as needed for maintenance)
  • Support requests and communication with the Avista team

1.2 Automatically collected data

To keep your websites healthy and secure, Avista Care may automatically collect technical information such as:

  • Website performance metrics
  • Security scan results
  • Update logs (plugins, themes, CMS core)
  • Error messages or crash logs
  • Hosting environment details (PHP version, server type, etc.)

1.3 Backups & maintenance data

If your plan includes backups or syncing:

  • Your website data may be stored securely for the purpose of backup restoration.
  • Backups are encrypted and deleted after their retention period.

2. How We Use the Information

We use collected information to:

  • Operate and maintain Avista Care
  • Monitor website health, uptime, and performance
  • Keep websites updated and secure
  • Provide customer support
  • Improve the Service
  • Manage billing and subscriptions
  • Detect, prevent, or address technical issues or misuse

We do not sell your data or use it for advertising.

3. Information Sharing

We only share your information when necessary:

3.1 Trusted service providers

Certain tools or systems help us operate the Service (e.g., hosting, monitoring services, security scanners, payment processors).
These partners only receive the minimum data required and must follow confidentiality and security obligations.

3.2 Legal requirements

We may share information if required by law, regulation, or to protect Avista, our users, or the public.

3.3 No selling, trading, or profiling

Avista does not sell, rent, or trade personal data.
We do not use your website data for external AI training, advertising, or profiling.

4. Data Security

We take security seriously and use industry-standard measures to protect your data, including:

  • Encrypted communication (HTTPS)
  • Secure backup storage
  • Access controls and authentication
  • Regular security monitoring

No system is completely risk-free, but we work continuously to keep your information protected.

5. Data Retention

We retain different types of data for different periods:

  • Account information: kept while your subscription is active
  • Backups: deleted after the plan-specific retention period
  • Support logs: kept for internal reference and service improvement
  • Technical logs: kept only as long as necessary for diagnostics

If you close your account, we delete or anonymize your data within a reasonable period unless legal obligations require longer storage.

6. Your Rights

Depending on your location (e.g., Iceland/EU), you have rights such as:

  • Access your personal data
  • Request correction or deletion
  • Export your data
  • Object to certain types of processing
  • Withdraw consent (where applicable)

To exercise these rights, contact us at the email address on our website.

7. Cookies & Tracking

Avista Care may use cookies or similar technologies to:

  • Keep you logged into your dashboard
  • Remember preferences
  • Improve functionality
  • Measure usage patterns

You can control cookies through your browser settings.

8. Children’s Privacy

The Service is not intended for individuals under 16.
We do not knowingly collect personal data from children.

9. International Data Transfers

If data is transferred outside Iceland or the EEA, we use safeguards such as:

  • Standard Contractual Clauses (SCCs)
  • GDPR-compliant processors
  • Adequate protection measures

10. Changes to This Privacy Policy

We may update this Privacy Policy from time to time.
If the changes are significant, we will notify you (e.g., email or dashboard message).
Continued use of the Service means you accept the updated policy.

Trusted service providers (“Sub-processors”)

Last Updated: 5th of January, 2026

Avista works with a small set of trusted service providers (“Sub-processors”) who help us deliver Avista Care and related services. Each provider is vetted for strong security practices, GDPR compliance, and data-handling standards. They only access the minimum data needed for their purpose.

Below is the full list of current Sub-processors, grouped by category.

1. Hosting & Infrastructure

Purpose: Cloud hosting for Avista services and dashboard infrastructure.
Data processed: Encrypted backups, logs, technical metadata.
Region: EU or US (with SCCs where needed).

Purpose: Storage of backups, documents, media, and Avista Chat files.
Data processed: Backups, uploaded documents, embeddings, system logs.
Region: EU/US.

Cloud provider

Engineering

Hosting Services

2. AI & Document Processing

Purpose: AI model inference for generating chatbot responses.
Data processed: Chat messages, user prompts, text from uploaded content.
Note: Data is not used to train external models; processed only for your bot.

Purpose: AI model inference for generating chatbot responses.
Data processed: Chat messages, user prompts, text from uploaded content.
Note: Data is not used to train external models; processed only for your bot.

Purpose: AI Service inference for generating chatbot responses.
Data processed: Chat messages, user prompts, text from uploaded content.
Note: Data is not used to train external models; processed only for your bot.

Purpose: Stores encoded vectors of documents for semantic search.
Data processed: Embeddings (mathematical representations), not raw files.

Purpose: Converts uploaded customer documents into searchable embeddings.
Data processed: Document text and structured content during processing.

3. Website Monitoring, Performance & Security

Purpose: Hosting Platform, Site monitoring, performance auditing, security scanning, uptime reports.
Data processed: Site URLs, uptime status, plugin/theme versions, security scan logs.
Region: US/EU (with GDPR-compliant safeguards).

You can create a new account at the end of the order process or on the following page. You can view all of your orders and subscriptions in your customer account. You can also change your addresses and your password.

Security
Continuous security and compliance monitoring

Purpose: DNS management, CDN performance, bot protection, and firewall security.
Data processed: IP addresses, request logs, traffic metadata.

4. Integrations & Workflow Automation

Purpose: Complex integrations and automation of workflows between Avista services and external apps (optional per customer).
Data processed: Whatever data the customer chooses to sync (e.g., customer info, orders, financial data or inventory, support request info).

Purpose: Automation of workflows between Avista services and external apps (optional per customer).
Data processed: Whatever data the customer chooses to sync (e.g., form submissions, support request info).

5. Email, Communication & Notifications

Purpose: Transactional emails such as password resets, notifications, alerts.
Data processed: Email addresses, message metadata.

6. Analytics & Dashboard Insights

Purpose: Product analytics.
Data processed: User usage data and metadata.

Purpose: Client and Avista Care Website Analytics
Data processed: User usage data and metadata.

Purpose: Server Level Analytics.
Data processed: General traffic info and server statistics.

7. Billing & Subscription Management

Purpose: Payment processing and subscription management.
Data processed: Billing details, transaction metadata (Avista does not store card numbers).

Purpose: Payment processing and subscription management.
Data processed: Billing details, transaction metadata (Avista does not store card numbers).

Purpose: Payment processing and subscription management.
Data processed: Billing details, transaction metadata (Avista does not store card numbers).

8. Internal Avista Operations

Self-hosted Project Management System

Communication and Project Management: Google Workspace is a cloud-based subscription service from Google that bundles professional, secure, and collaborative productivity tools, including Gmail, Docs, Drive, Calendar, and Meet. 

How We Choose Sub-Processors

Every provider must meet standards for:

  • GDPR compliance
  • Strong data security
  • Limited access
  • Clear purpose
  • Contractual protection
  • Transparent operations

We update this list whenever new providers are added or removed, and we notify customers as required by our DPA.