Avista Care & Avista Chat – Data Processing Agreement (DPA)

Last Updated: 1st of December, 2025

This Data Processing Agreement (“DPA”) forms part of the Terms of Service or any other written or electronic agreement between the Customer (“Controller”) and Avista (“Processor”) for the use of Avista Care and Avista Chat (the “Services”).

This DPA ensures compliance with the EU General Data Protection Regulation (GDPR) and governs how Avista processes personal data on behalf of the Customer.

1. Definitions

  • “Controller” means the Customer who determines the purposes and means of processing personal data.
  • “Processor” means Avista, which processes personal data on behalf of the Controller.
  • “Personal Data” means any information relating to an identified or identifiable natural person.
  • “Processing” means any operation performed on personal data, such as collection, storage, transmission, or deletion.
  • “Sub-processor” means any third-party processor engaged by Avista.
  • “Services” means Avista Care (website maintenance & monitoring) and Avista Chat (AI chatbot services).

2. Scope of Processing

Avista processes personal data solely for the following purposes:

Avista Care

  • Website monitoring, updates, backups, and performance services
  • Logging and diagnostics
  • Security scanning
  • Customer support

Avista Chat

  • Training and operating chatbots using customer-provided data
  • Handling prompts, messages, logs, and uploaded documents
  • Monitoring usage and performance
  • Providing support and analytics

Avista processes data only according to the Controller’s documented instructions.

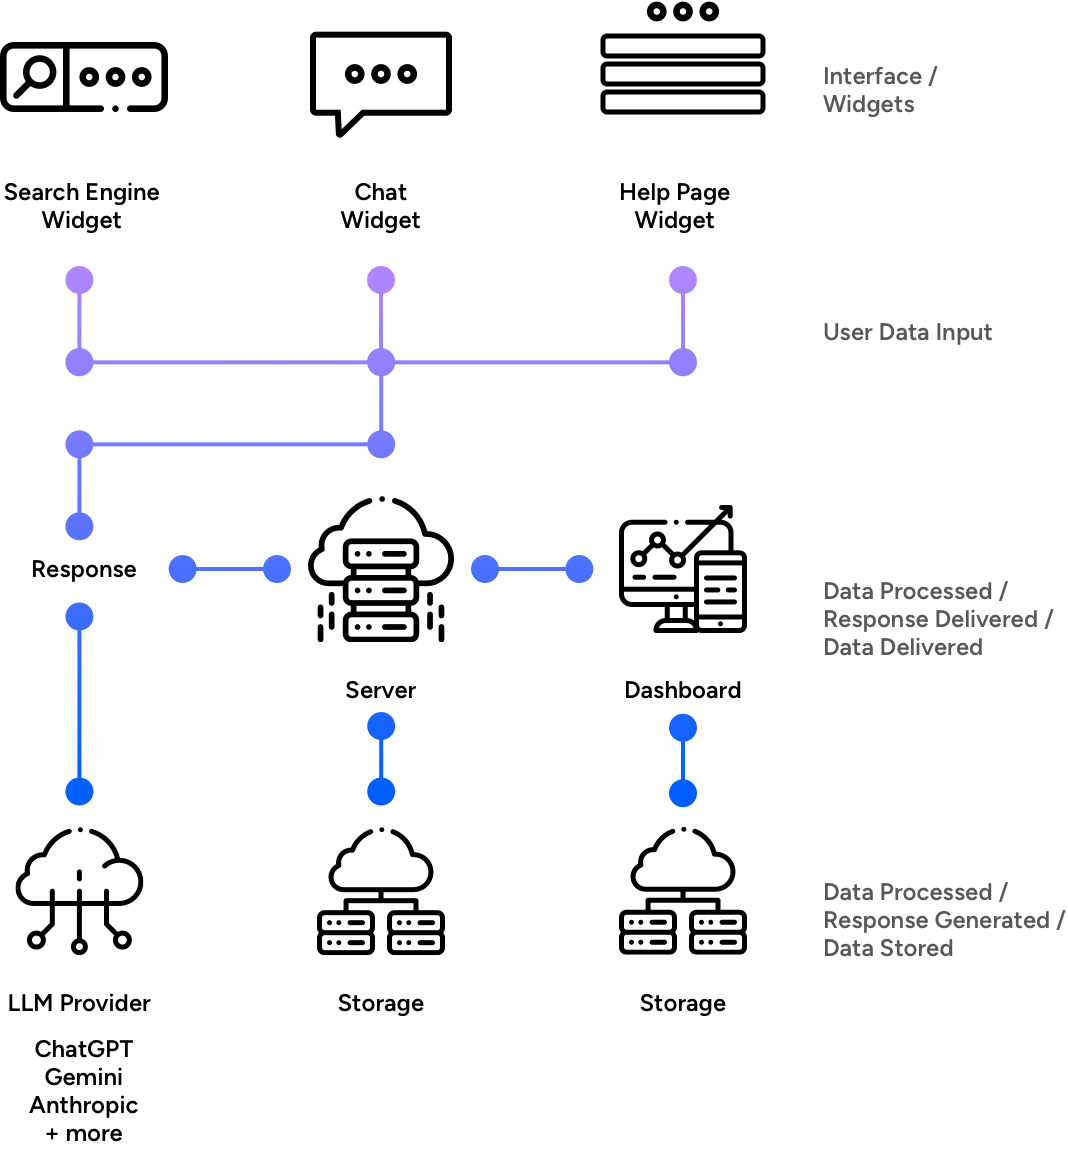
Overview of Avista Chat data flow:

3. Types of Data Processed

Depending on the Services used, Avista may process:

  • Contact details (e.g., name, email)
  • Website metadata (domains, logs, security scan results)
  • Backup data and content from Customer websites
  • Chat messages, uploaded documents, or AI training inputs (Avista Chat)
  • Technical information (IP addresses, browser data, error logs)
  • Billing information (handled by payment processors)

Avista does not use Customer data to train external AI models or for advertising.

4. Duration of Processing

Processing continues for the duration of the Customer’s subscription and is limited to what is needed to deliver the Services. Upon termination, Avista deletes or anonymizes data in accordance with Section 10.

5. Obligations of the Processor (Avista)

Avista agrees to:

  • Process data only on Controller’s instructions
  • Maintain confidentiality
  • Implement appropriate technical and organizational security measures
  • Assist the Controller in fulfilling GDPR obligations
  • Notify Controller of data breaches without undue delay
  • Keep updated records of processing activities
  • Ensure employees and contractors follow security and privacy policies

6. Sub-Processors

The Controller authorizes Avista to use Sub-processors for hosting, backups, monitoring, AI inference, analytics, and support tools.
Avista will:

  • Only engage GDPR-compliant Sub-processors
  • Ensure each Sub-processor is bound by equivalent data protection obligations
  • Publish or provide a list of Sub-processors upon request
  • Inform the Controller of any significant changes to Sub-processors

The Controller may object to a Sub-processor on reasonable grounds.

7. Obligations of the Controller (Customer)

The Controller agrees to:

  • Ensure their processing instructions comply with GDPR
  • Provide data that they have the right to process
  • Not upload unlawful or sensitive personal data unless necessary
  • Maintain accurate configuration and access controls
  • Inform Avista of any inaccuracies or corrections needed

8. Data Subject Rights

Avista will assist the Controller in responding to requests such as:

  • Access
  • Rectification
  • Erasure
  • Portability
  • Restriction
  • Objection

Avista will not respond directly to the data subject unless instructed by the Controller.

9. Security Measures

Avista implements industry-standard measures including:

  • Encryption in transit
  • Encrypted storage for backups
  • Secure access controls and authentication
  • Regular security monitoring
  • Segmented infrastructure
  • Data minimization
  • Least-privilege access policies

A full description of measures can be provided upon request.

10. Return or Deletion of Data

When the Service ends:

  • Access to dashboards is removed
  • Backups are deleted after retention expires
  • Personal data is erased or anonymized within a reasonable period
  • Logs may be retained temporarily for security or compliance

The Controller may request accelerated deletion.

11. International Transfers

If data is transferred outside the EEA:

  • Avista uses GDPR-approved safeguards such as Standard Contractual Clauses (SCCs)
  • Only processors with adequate protection levels are engaged
  • Transfers comply with applicable laws

12. Breach Notification

If Avista becomes aware of a data breach affecting Customer data, Avista will:

  • Notify the Controller without undue delay
  • Provide available information on the nature of the breach
  • Support the Controller in fulfilling notification duties

13. Audits & Compliance

  • Avista will provide documentation needed to demonstrate compliance
  • Formal audits may be requested with reasonable notice
  • Audits must respect confidentiality and technical boundaries

14. Liability

Both parties’ liability follows the main Terms of Service.
Avista is only liable for processing operations under its direct control.

15. Governing Law

This DPA is governed by the laws of Iceland and applicable EU/EEA data protection regulations (including GDPR).

Questions or Concerns?

If you want more detail about our services, your privacy or how we handle data, you can contact us through our website.